Authentication User Credentials
Description
Use delegated access (User Credentials) whenever you want to let a signed-in user work with their own resources or resources they can access. Whether it's an admin setting up policies for their entire organization or a user deleting an email in their inbox, all scenarios involving user actions should use delegated access. [API reference]
Instructions
Follow these simple steps below to create Microsoft Entra ID application with delegated access:
automation@my-company.com).
When you use a personal account which is tied to a specific employee profile and that employee leaves the company,
the token may become invalid and any automated processes using that token will start to fail.
- Navigate to the Azure Portal and log in using your credentials.
- Access Microsoft Entra ID.
-
Register a new application by going to
App registrations
and clicking on New registration button:
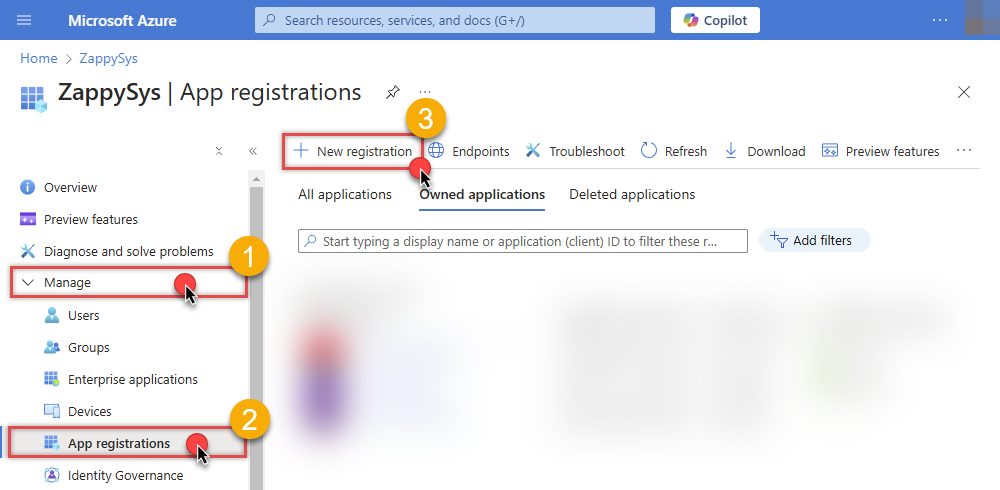 INFO: Find more information on how to register an application in Graph API reference.
-
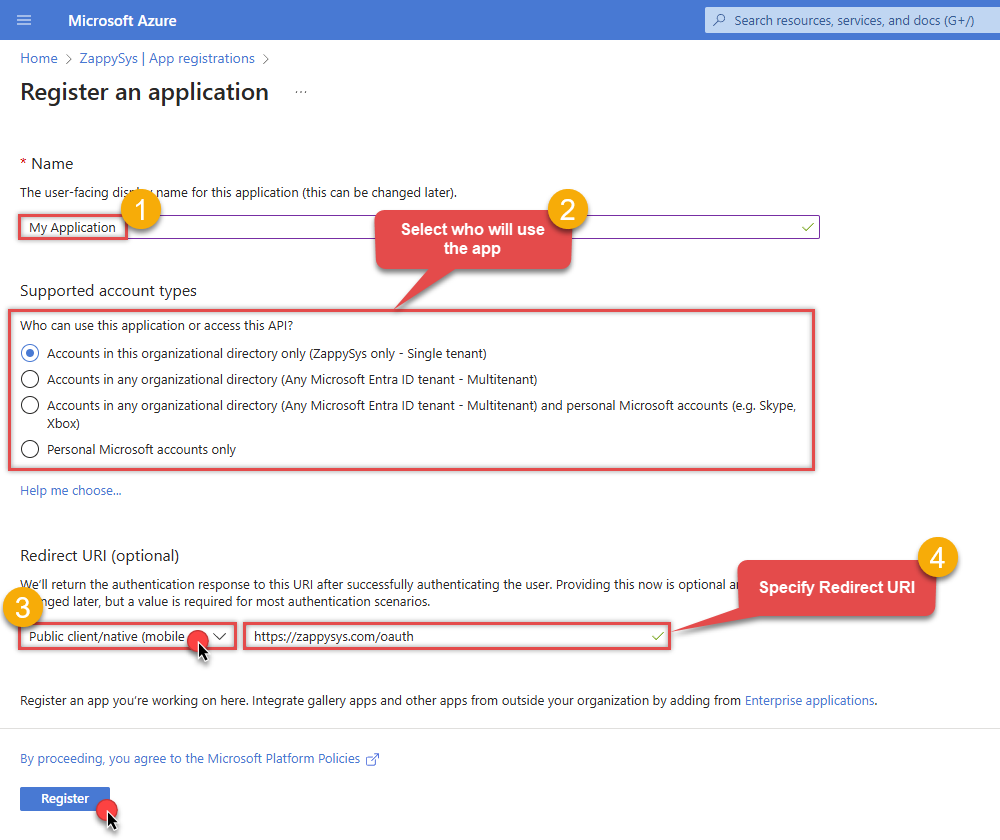
When configuration window opens, configure these fields:
-
Supported account type
- Use
Accounts in this organizational directory only, if you need access to data in your organization only.
- Use
-
Redirect URI:
- Set the type to
Public client/native (mobile & desktop). - Use
https://zappysys.com/oauthas the URL.
- Set the type to
-
Supported account type
-
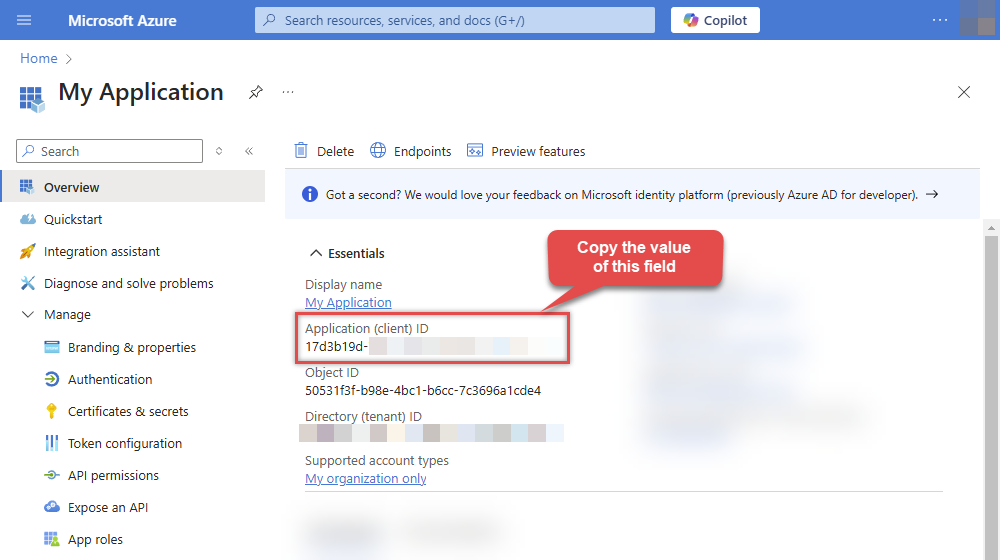
After registering the app, copy the Application (client) ID for later:
-
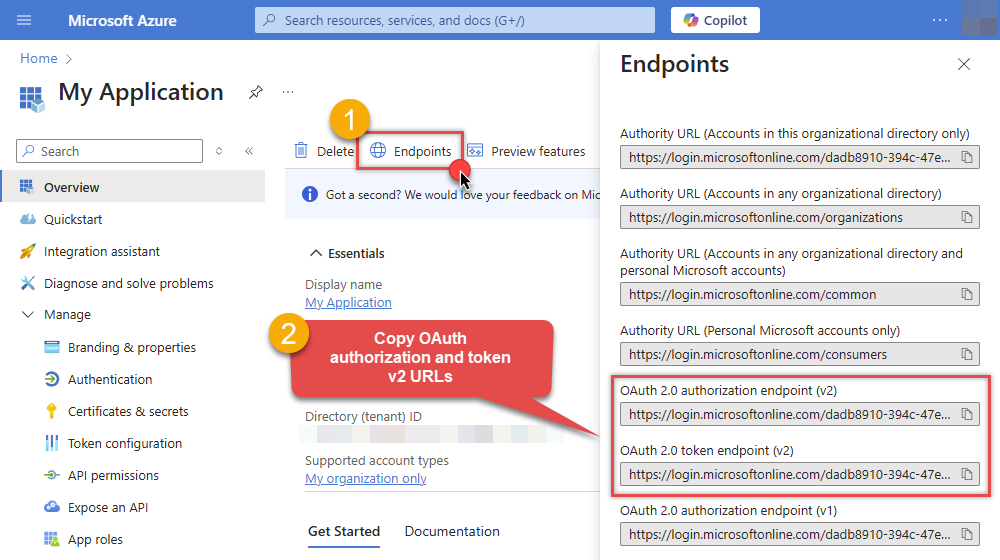
Then copy OAuth authorization endpoint (v2) & OAuth token endpoint (v2) URLs to use later in the configuration:
-
Now go to SSIS package or ODBC data source and use the copied values in User Credentials authentication configuration:
- In the Authorization URL field paste the OAuth authorization endpoint (v2) URL value you copied in the previous step.
- In the Token URL field paste the OAuth token endpoint (v2) URL value you copied in the previous step.
- In the Client ID field paste the Application (client) ID value you copied in the previous step.
-
In the Permissions (Scope) field use the default or pick labeled permissions. [User] scopes are enough for your own OneDrive (read-only:
Files.Read). [Tenant] entries are broader and often need an admin to approve the app—use them when resolving other users’ or groups’ drives (User.Read.All,Group.Read.All) or all reachable files (Files.Read.All/Files.ReadWrite.All).-
offline_access,openid,profile -
User.Read,Files.Read,Files.ReadWrite -
Files.Read.All,Files.ReadWrite.All,User.Read.All,Group.Read.All(often admin consent)
Admin consent note:- Token generation can still ask for admin approval, even when delegated scopes are listed in API permissions.
- A Global Administrator can allow user consent for selected low-impact delegated permissions.
- Broad scopes such as
Files.Read.All,Files.ReadWrite.All,User.Read.All, andGroup.Read.Allmay still require admin consent.
-
- Press Generate Token button to generate Access and Refresh Tokens.
- Optional step. Choose Default Drive Id from the drop down menu.
- Click Test Connection to confirm the connection is working.
- Done! Now you are ready to use the API Connector!
Parameters
| Parameter | Required | Default value | Options | ||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
Name:
Label: Authorization URL |
YES |
|
|||||||||||||||||||||||
|
Name:
Label: Token URL |
YES |
|
|||||||||||||||||||||||
|
Name:
Label: Application (client) ID |
YES | ||||||||||||||||||||||||
|
Name:
Label: Permissions (Scope) Microsoft Graph delegated scopes for OneDrive (Graph API). [System] = refresh token and sign-in (offline_access, openid, profile). [User] = signed-in user only—use Files.Read or Files.ReadWrite for lower-impact read-only or read/write. [Tenant] = broader .All and directory permissions that Microsoft documents as typically requiring admin consent (Files.Read.All, Files.ReadWrite.All, User.Read.All, Group.Read.All). Add User.Read.All and Group.Read.All when listing other users’ or groups’ drives. Tenant policies may still affect consent. |
YES |
offline_access~Files.Read~Files.Read.All~Files.ReadWrite~Files.ReadWrite.All~openid~profile~User.Read
|
|
||||||||||||||||||||||
|
Name:
Label: Client Secret |
|||||||||||||||||||||||||
|
Name:
Label: Refresh Token File Path If you cant fit long refresh token in ConnectionString from your program then use this. Supply three properties in json format (i.e. save this in file { "access_token": "YOUR_ACCESS_TOKEN", "refresh_token": "YOUR_REFRESH_TOKEN", "expires_in": 3600 } ) |
|||||||||||||||||||||||||
|
Name:
Label: Return URL |
https://zappysys.com/oauth
|
|
|||||||||||||||||||||||
|
Name:
Label: Default Group or User Id (additional Scopes needed to list - If fails enter manually) To list all users and groups from your organizations you need additional scopes. See connection UI - Choose User.Read.All and Group.Read.All Scopes and regenerate token. You can manually type value too if you know Group or User Id. Format is /users/{id} OR /groups/{id} |
|
||||||||||||||||||||||||
|
Name:
Label: Default Drive Id (Select after clicking **Generate Token**) |
me
|
||||||||||||||||||||||||
|
Name:
Label: RetryMode |
RetryWhenStatusCodeMatch
|
|
|||||||||||||||||||||||
|
Name:
Label: RetryStatusCodeList 429 is API limit reached, 423 is File locked |
429|503|423
|
||||||||||||||||||||||||
|
Name:
Label: RetryCountMax |
5
|
||||||||||||||||||||||||
|
Name:
Label: RetryMultiplyWaitTime |
True
|
||||||||||||||||||||||||
|
Name:
Label: Login Prompt Option Choose this if you want to force login prompt or permission prompt. |
|
||||||||||||||||||||||||
|
Name:
Label: Search Option For Non-Indexed Fields (Default=Blank - Search Only Indexed) If you wish to do certain operations e.g. search / order by on non-indexed fields then you have to set this option to HonorNonIndexedQueriesWarningMayFailRandomly. By default filter / orderby on non-indexed fields not allowed. |
|
||||||||||||||||||||||||
|
Name:
Label: Extra Headers (e.g. Header1:AAA||Header2:BBB) |
|
||||||||||||||||||||||||
|
Name:
Label: IsAppCred For internal use only |
0
|