
Authentication User Credentials
Description
Use delegated access (User Credentials) whenever you want to let a signed-in user work with their own resources or resources they can access. Whether it's an admin setting up policies for their entire organization or a user deleting an email in their inbox, all scenarios involving user actions should use delegated access. [API reference]
Instructions
Follow these simple steps below to create Microsoft Entra ID application with delegated access:
automation@my-company.com).
When you use a personal account which is tied to a specific employee profile and that employee leaves the company,
the token may become invalid and any automated processes using that token will start to fail.
- Navigate to the Azure Portal and log in using your credentials.
- Access Microsoft Entra ID.
-
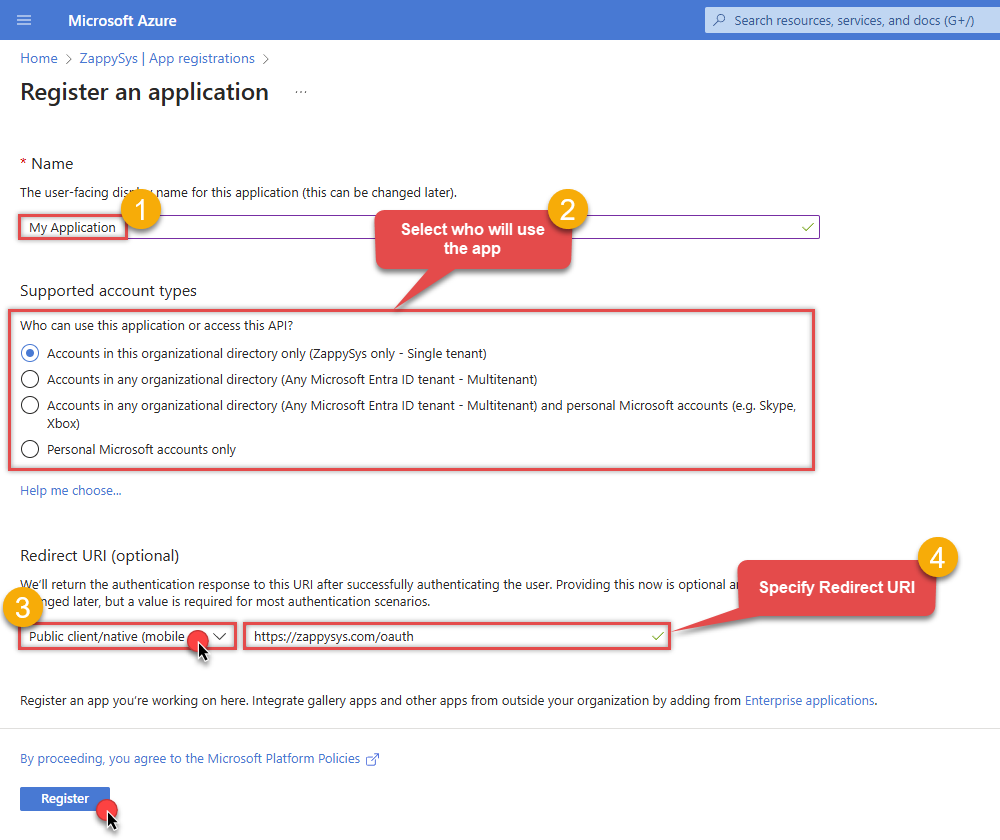
Register a new application by going to App registrations and clicking on New registration button:
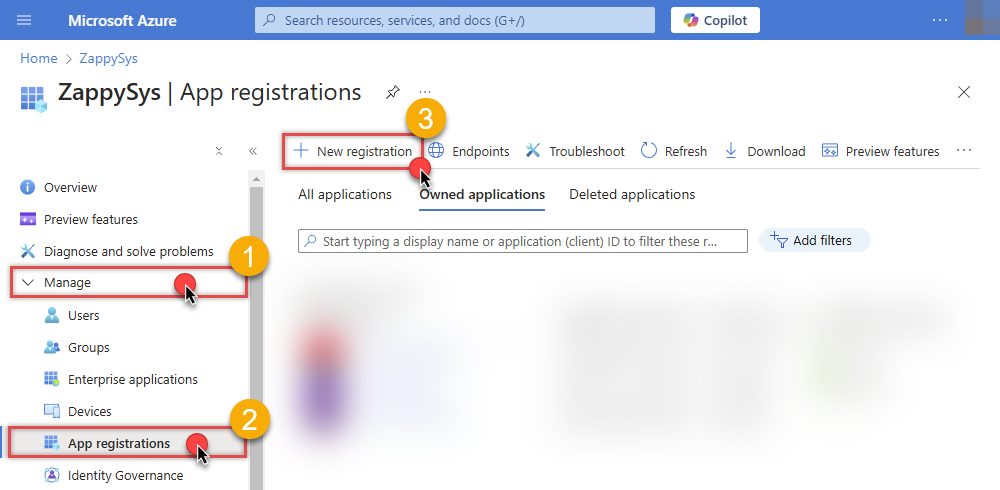 INFO: Find more information on how to register an application in Graph API reference.
-
When configuration window opens, configure these fields:
-
Supported account type
- Use
Accounts in this organizational directory only, if you need access to data in your organization only.
- Use
-
Supported account type
-
Redirect URI:
- Set the type to
Public client/native (mobile & desktop). - Use
https://zappysys.com/oauthas the URL.
- Set the type to
-
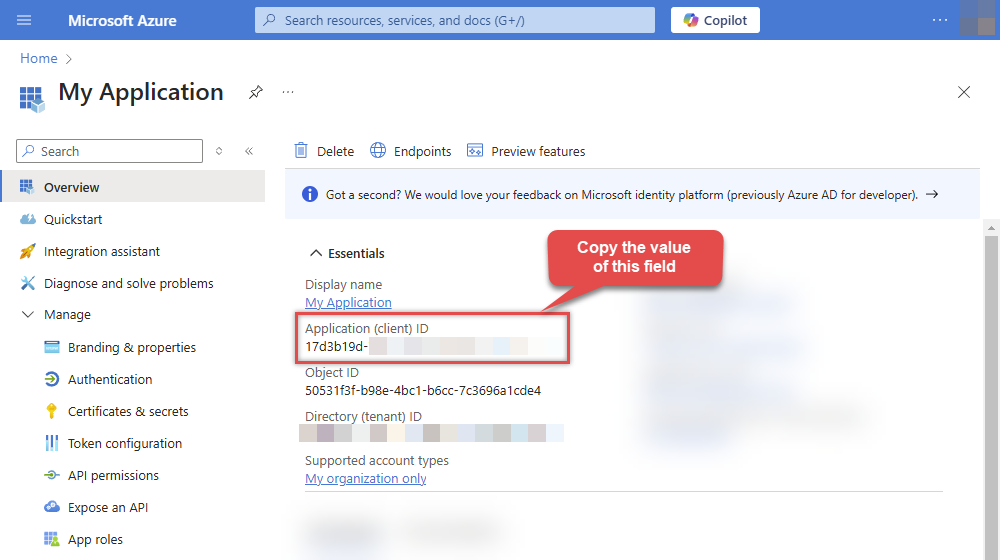
After registering the app, copy the Application (client) ID for later:
-
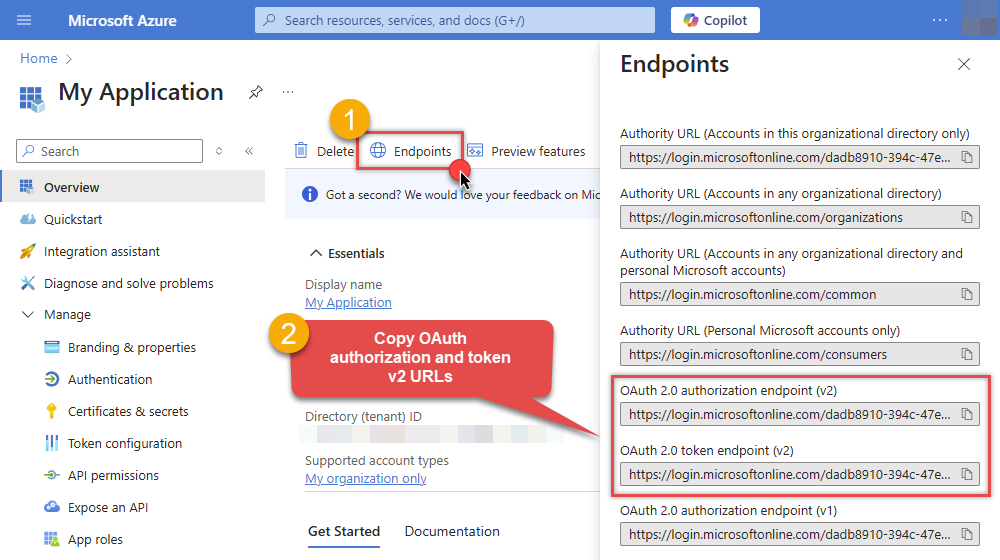
Copy OAuth authorization endpoint (v2) & OAuth token endpoint (v2) URLs to use later in the configuration:
-
Now go to SSIS package or ODBC data source and use the copied values in User Credentials authentication configuration:
- In the Authorization URL field paste the OAuth authorization endpoint (v2) URL value you copied in the previous step.
- In the Token URL field paste the OAuth token endpoint (v2) URL value you copied in the previous step.
- In the Client ID field paste the Application (client) ID value you copied in the previous step.
-
In the Scope field use the default or pick labeled permissions. Prefer
User.Read,Files.Read, orFiles.ReadWritewhen you want lower-impact, user-consent-friendly access; addSites.*.All/Files.*.Allonly when you need full site or file coverage (those often need an admin to approve the app for the organization).-
offline_access -
openid -
profile -
User.Read -
Sites.ReadWrite.All -
Files.ReadWrite.All
Admin consent note:- Token generation can still ask for admin approval, even when delegated scopes are listed in API permissions.
- A Global Administrator can allow user consent for selected low-impact delegated permissions.
- Broad scopes such as
Sites.Read.All,Sites.ReadWrite.All,Files.Read.All, andFiles.ReadWrite.Allmay still require admin consent.
-
- Press Generate Token button to generate Access and Refresh Tokens.
- Optional step. Choose Default Site Id from the drop down menu.
- Click Test Connection to confirm the connection is working.
- Done! Now you are ready to use the API Connector!
Parameters
| Parameter | Required | Default value | Options | ||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
Name:
Label: Authorization URL |
YES |
|
|||||||||||||||||||||||||||||||||
|
Name:
Label: Token URL |
YES |
|
|||||||||||||||||||||||||||||||||
|
Name:
Label: Application (client) ID |
YES | ||||||||||||||||||||||||||||||||||
|
Name:
Label: Permissions (Scope) OAuth scopes for this connection: Automatic re-auth uses offline_access (refresh token). OpenID and Profile are standard sign-in claims. Basic user info is User.Read (Graph). [Tenant] entries are Graph delegated permissions with a .All suffix—broad tenant-wide access that often requires admin consent. [User] entries marked Files.Read / Files.ReadWrite are Graph file permissions for the signed-in user (including Teams libraries). [User] entries with https://[YOUR-SITE].sharepoint.com/... are SharePoint resource scopes: replace [YOUR-SITE] with your tenant web hostname only (e.g. contoso for contoso.sharepoint.com—no brackets, no path). If you mix Graph and SharePoint URL scopes, ensure your app registration exposes the permissions you select and that the access token audience matches the API you call (Graph vs SharePoint REST). |
YES |
offline_access~Files.ReadWrite.All~openid~profile~Sites.ReadWrite.All~User.Read
|
|
||||||||||||||||||||||||||||||||
|
Name:
Label: Return URL |
YES |
https://zappysys.com/oauth
|
|
||||||||||||||||||||||||||||||||
|
Name:
Label: Default Site Id (select after pressing 'Generate Token') Specify a default site you like to use for operations. You can always override this for various operations. Selection of this parameter needs at minimum Sites.Read.All permission otherwise it will fail to list all sites. If it fails, please enter SiteId manually. You can find SiteId by visiting this URL in browser (assuming you visted SharePoint site and already logged in) https://{your-company}.sharepoint.com/_api/site --OR-- for sub-site use https://{your-company}.sharepoint.com/sites/{your-site}/_api/site. Find Id from the response (e.g. |
YES |
root
|
|||||||||||||||||||||||||||||||||
|
Name:
Label: Client Secret |
|||||||||||||||||||||||||||||||||||
|
Name:
Label: Default Drive Id (select after pressing 'Generate Token') Specify a default Drive Id you like to use for operations. |
|||||||||||||||||||||||||||||||||||
|
Name:
Label: Login Prompt Option Choose this if you want to force login prompt or permission prompt. |
|
||||||||||||||||||||||||||||||||||
|
Name:
Label: RetryMode |
RetryWhenStatusCodeMatch
|
|
|||||||||||||||||||||||||||||||||
|
Name:
Label: RetryStatusCodeList 429 is API limit reached, 423 is File locked |
429|503|423
|
||||||||||||||||||||||||||||||||||
|
Name:
Label: RetryCountMax |
5
|
||||||||||||||||||||||||||||||||||
|
Name:
Label: RetryMultiplyWaitTime |
True
|
||||||||||||||||||||||||||||||||||
|
Name:
Label: Search Option For Non-Indexed Fields (Default=Blank - Search Only Indexed) If you wish to do certain operations e.g. search / order by on non-indexed fields then you have to set this option to HonorNonIndexedQueriesWarningMayFailRandomly. By default filter / orderby on non-indexed fields not allowed. |
|
||||||||||||||||||||||||||||||||||
|
Name:
Label: Extra Headers (e.g. Header1:AAA||Header2:BBB) |
|
||||||||||||||||||||||||||||||||||
|
Name:
Label: IsAppCred For internal use only |
0
|